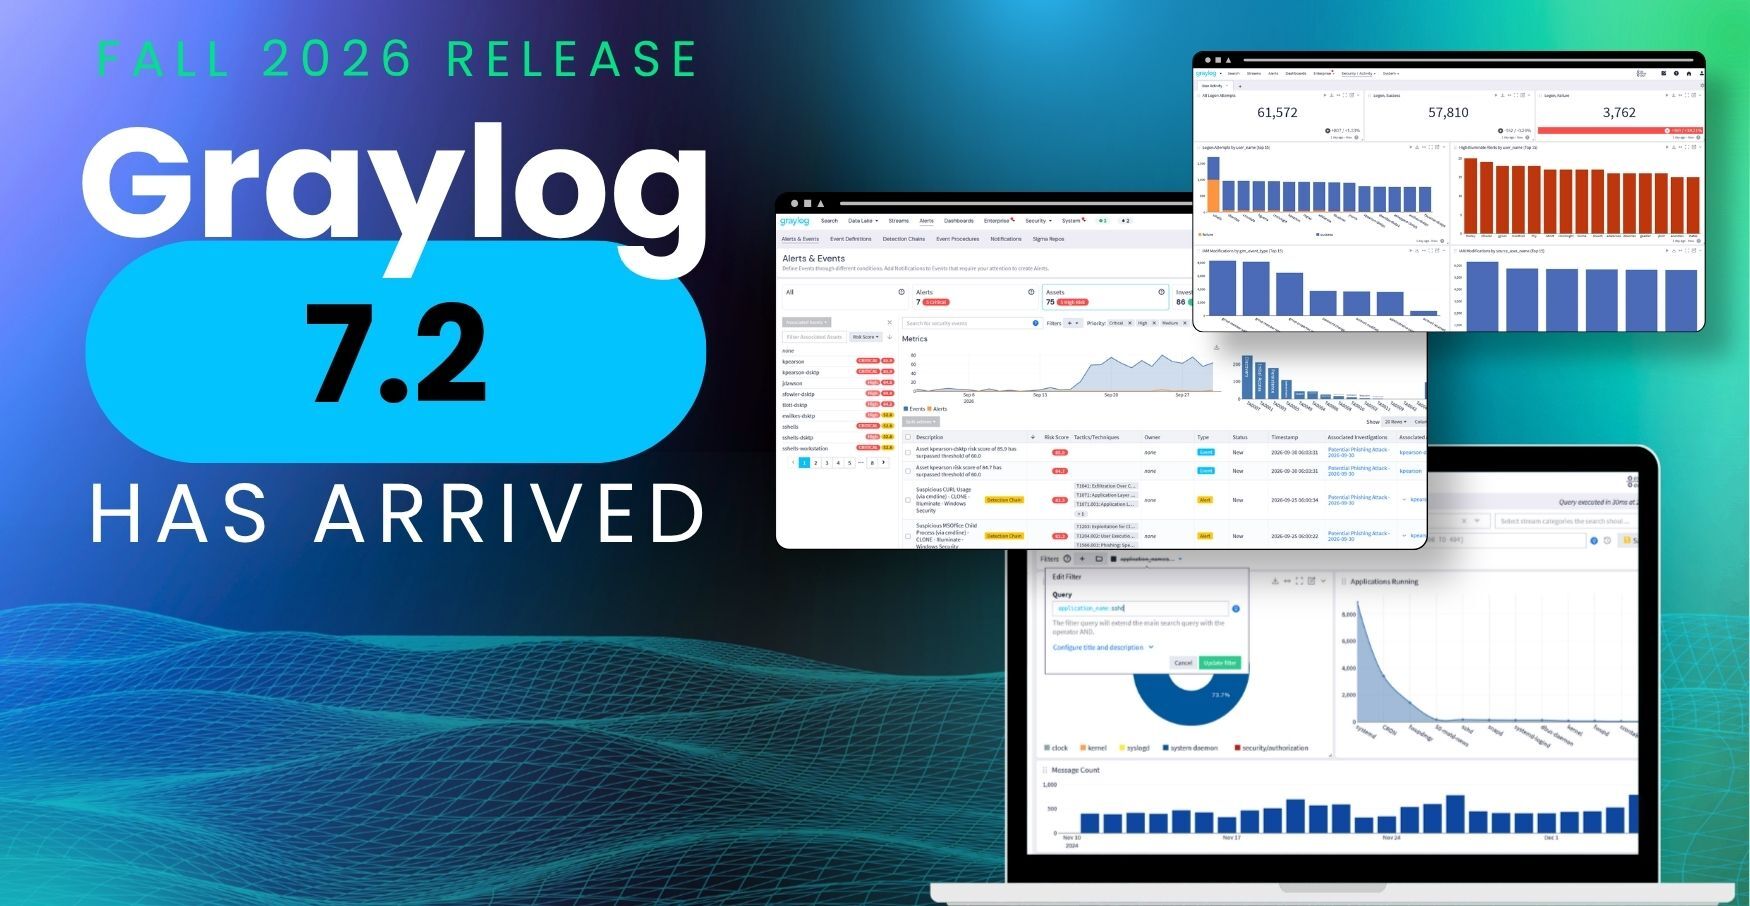
It is with real excitement, and no small amount of pride, that I get to introduce Graylog 7.2.
This release is built around three challenges analysts and platform administrators face every day: alert overload from AI-accelerated threats, the operational weight of managing a SIEM, and the friction of getting usable data in cleanly.
- Challenge #1: How Does Graylog 7.2 Turn Alert Fatigue Into Case-Based Triage
- Challenge #2: What New Tools Does Graylog 7.2 Add for Platform Administrators?
- Challenge #3: What Is the Graylog Collector in Version 7.2?
How Does Graylog 7.2 Turn Alert Fatigue Into Case-Based Triage?
Challenge #1: Security operations are already strained, and AI just gave threat actors a cheat code?
- AI-generated phishing achieves a 54% click-through rate
- Nearly half of every analyst’s workload generates zero security value.
- 75% of analysts report no time left for proactive threat hunting
If you are feeling overwhelmed, you are not alone. Our goal is to shift under-resourced teams from an alert-based triage experience (that’s fundamentally flawed) to a case-based triaged experience, where Graylog automatically assembles and prioritizes the investigation for you.
Previous releases built on this idea by introducing composite asset risk scoring and automatic investigation creation. In 7.2, we added actions on the Welcome and Alerts page to help you transition from event-based triage to case-based triage. And we have introduced new automation with an embedded agentic framework.
- The Asset Risk Triage Agent evaluates your high-risk assets, analyzing the events contributing to the high-risk score, assessing their contribution or for false positives, and adding pertinent logs as evidence into the Investigation, and generating an immediate assessment. This starts the investigation with a full picture and context vs beginning with a single piece of evidence while also focusing on AI’s context window to increase accuracy of its insights and assessments.
- The Event Tuning Advisor evaluates the events you have flagged as a false positive and provides tuning guidance with one-click enablement. This agent reviews the group-by fields for both when the event was true (if any) and false to make its determinations, saving analysts time determine how to tune events for greater accuracy.
After initial triage, the human analyst can take advantage of new Sankey and Network graph visualizations to understand relationships faster than data tables.
The system is an orchestration of our detection capabilities, risk-scoring algorithms, intelligent event consolidation, and agentic workflows aligned to identify corroborated evidence of an active incident that deserves a human’s attention. This is what we are calling the “Verascend™ Incident System”.

How Does Graylog 7.2 Reduce Time Spent on Platform Administration?
Challenge #2: Managing a SIEM platform is a challenge in itself
While Graylog provides alternatives for your platform management (Graylog Cloud, Graylog’s MSSP/MDR partners), we also serve the largest population of self-managed SIEM in the world. Many Graylog users want the autonomy to operate Graylog on their own infrastructure and manage what data goes where and for how long.
Yet, time is a luxury most of us can’t afford to spend on platform administration. We continue to invest in capabilities that allow you to proactively spotlight developing issues and address them before they become operation headaches.
- Additional resource details on your Graylog and Data nodes, including an ability to enable MongoDB profiling to identify slow queries and troubleshoot performance issues.
- Streams performance views and Pipeline debugging metrics pinpoint resource-over usage.
- Warm tier management page reducing time to take advantage of less expensive storage options without sacrificing visibility.
- A Health Panel that grades your internal component health, providing troubleshooting tips and direct links to tackle warning and down states.
How Does Graylog 7.2 Give Teams Direct Control Over Data Collection?
Challenge 3: Making data useful
Graylog has consistently received positive feedback that it is pretty quick to get it up and running with your data. And yet we found a way to make it even faster and easier to maintain. Getting the right data has depended on agents and collectors that someone else builds and maintains, which does come with complexity.
In 7.2, we’re introducing a preview of the Graylog Collector, a native, Graylog-built collection agent that gives you direct control over what data flows in, how it’s handled, and where it comes from, without depending on third-party tooling. We’re sharing this early because we want your input as it develops.
Where Can Teams Explore the Full Graylog 7.2 Release?
This only scratches the surface of what shipped in 7.2.
Install a fresh instance of Graylog and you will find a new onboarding experience built to get you up and running faster. Watchlists now tie into Spotlight content, so you can tune detections to your environment as soon as they land. New Warm Tier and Detection Chain management pages round out the release, giving Open, Enterprise, and Security users plenty more to explore.
I am excited to share this release with you, and I look forward to hearing what you think.
Cheers and happy hunting!

VP of Product Management