UEBA & Anomaly Detection Available in: Graylog Security — Compare Plans
Graylog AI is built to enhance your security team, not replace it. Machine learning surfaces unusual user and entity behavior, AI summaries turn dashboards and investigations into plain-language takeaways, and AI agents take on routine review and tuning work. An open MCP Server lets you bring your own AI tools to Graylog data, governed by the same permissions and audit trail as your analysts. Every insight is explainable, and people stay in control, without compromise.
Detect what rules miss. Understand it faster. Act with confidence.
Core AI Capabilities in Graylog:
Machine learning learns normal behavior and flags insider threats, credential misuse, and unusual data movement that static rules never catch.
AI summaries turn busy dashboards and complex investigations into plain-language findings and clear next steps.
Built-in agents handle asset review and detection tuning, while an open MCP Server connects your own AI tools to Graylog data.
Graylog applies AI where analysts lose the most time: spotting what doesn’t fit, making sense of what they find, and clearing routine work off their plate. Every capability respects your existing RBAC and audit logging, and shows the reasoning behind its output.
Expose unseen behavior risks. Graylog machine learning builds behavioral baselines for users, hosts, and applications, then flags deviations such as insider threats, credential misuse, and unusual data transfers. Each enabled detector creates its own event definition, so anomalies flow into your existing alerting.

UEBA & Anomaly Detection Available in: Graylog Security — Compare Plans
Get instant situational awareness from any dashboard. AI reads the widgets on screen and summarizes what stands out, such as spikes, shifts, and outliers, in plain language. Analysts and managers see what matters without interpreting every chart.
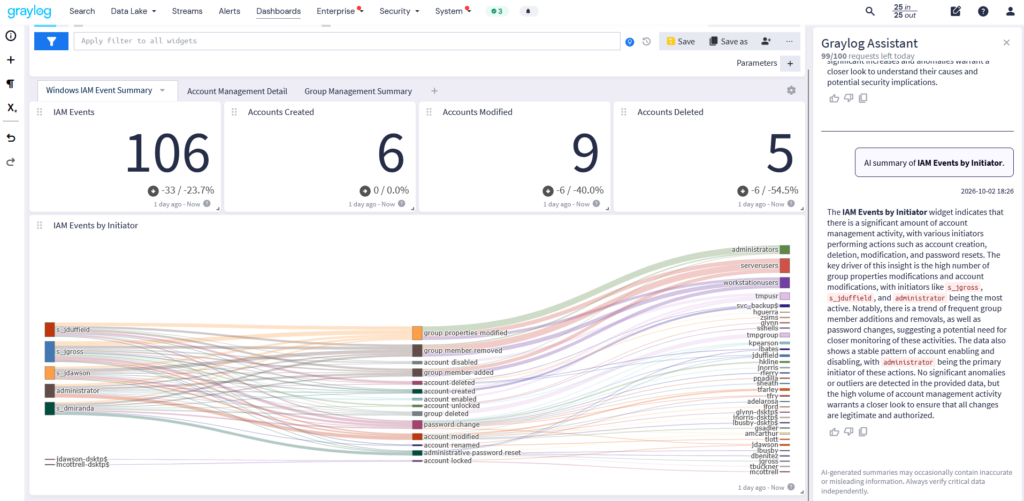
Dashboard Widget AI Summary Available in: Graylog Security | Graylog Enterprise — Compare Plans
Turn investigation evidence into a decision-ready report. AI reviews the events, logs, and notes attached to an investigation and produces a summary of what happened, what was affected, and what to do next.
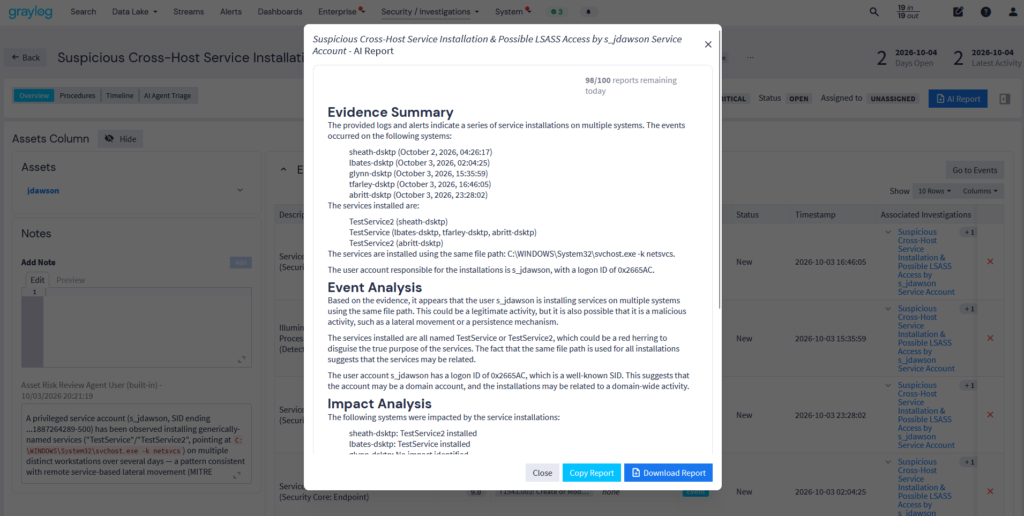
Investigation Report AI Summary Available in: Graylog Security — Compare Plans
Hand routine analysis to purpose-built AI agents. Graylog agents work inside your environment, on your data, and return recommendations for an analyst to approve. Nothing changes without a human decision.
Asset Review
Keep asset context current and actionable. The Asset Review agent examines an asset’s risk score, related events, and vulnerability data, then summarizes its security posture and recommends next steps.
Event Definition Tuning Advisor
Sharpen detections without hours of manual tuning. The Tuning Advisor reviews how event definitions have triggered over time, identifies noisy or low-value alerts, and recommends specific changes.
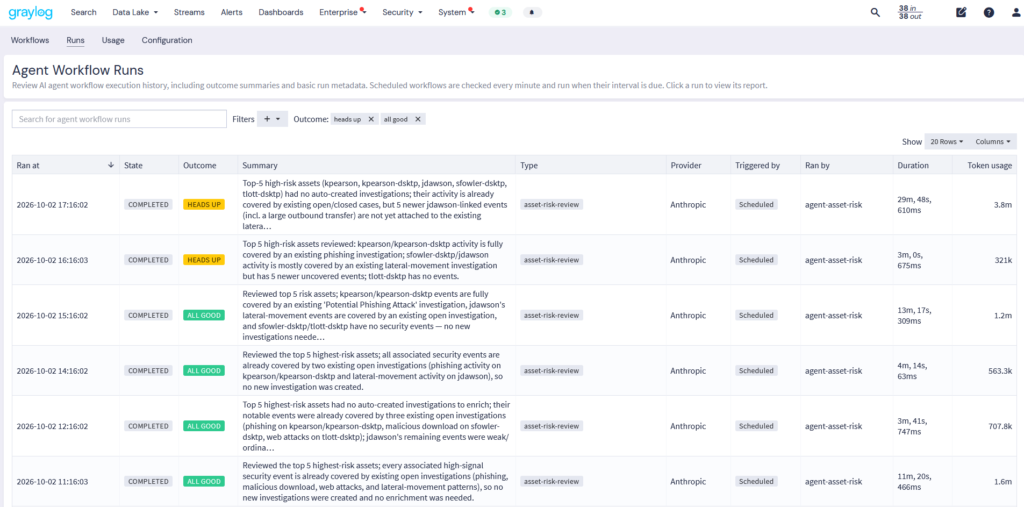
AI Agent Workflows Available in: Graylog Security | Graylog Enterprise — Compare Plans
Bring your own AI to Graylog data. Graylog’s MCP Server gives any MCP-compatible AI agent or LLM tool standardized access to logs, events, and alerts, with no custom integration work. External agents see only what your RBAC policies allow, and every interaction is written to the audit log.
Data Routing and Tiering Available in: Graylog Security | Graylog Enterprise | Graylog Open — Compare Plans
Security teams do not need science fiction. They need speed, signal, and confidence. At Graylog, our philosophy is simple: AI must be useful, explainable, and built to augment humans. It should automate repetitive tasks, enrich the important ones, and always show its work. That is why we invest in agentic capabilities that accelerate routine steps, add guardrails, and keep analysts in control.
With Graylog, AI is practical, accountable, and always without compromise.
Graylog uses AI across three stages of security work. Machine learning detects anomalous behavior, AI summaries explain dashboards and investigations in plain language, and AI agents handle routine work like asset review and detection tuning.
No. Graylog AI automates repetitive steps and recommends actions, while analysts make the decisions. Every output is explainable, and every action is auditable.
User and Entity Behavior Analytics (UEBA) uses machine learning to learn what normal looks like for users, hosts and applications. Graylog flags deviations, such as unusual logins, permission changes or data transfers, with a confidence score so analysts can prioritize them.
Dashboard summaries describe what stands out across the widgets you’re viewing. Investigation summaries turn the evidence in an investigation into a written report of what happened and recommended next steps.
They are purpose-built AI agents that run specific tasks inside Graylog. Asset Review assesses an asset’s risk and recommends follow-up. The Event Definition Tuning Advisor identifies noisy detections and recommends changes to reduce false positives.
No. Agents return recommendations for an analyst to review and approve, so detections and systems change only through a human decision.
It is a Model Context Protocol (MCP) endpoint that lets any MCP-compatible AI agent or LLM tool query Graylog logs, events and alerts through one standard protocol, without custom integration work.
Yes. MCP requests follow your existing Graylog RBAC permissions, so external agents only see data their assigned role allows. Every MCP interaction is recorded in the audit log.
Yes. Anomaly detection with confidence scoring, risk-based prioritization and the Event Definition Tuning Advisor all reduce alert noise and help analysts focus on genuine threats.
Graylog already delivers fast, accurate, schema-aware search. Analysts get precise results without the uncertainty of generative guesses.
AI features are available in Graylog Security and Graylog Enterprise, with some capabilities specific to Graylog Security. See Compare Plans for details.
Deep dive into AI-related features in Graylog


